

Indian Cybersecurity Researcher Nisarga Adhikary, Named in US DoJ Hall of Fame
| General Studies Paper I: Important Achievements |
Why in News?
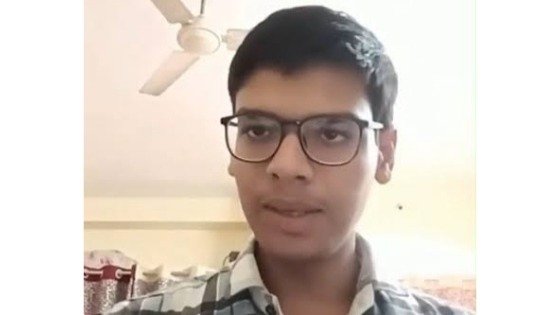
Recently, 19-year-old Indian cybersecurity researcher Nisarga Adhikary was named in the US DoJ Hall of Fame after responsibly reporting a critical vulnerability in a major law-enforcement system.
Who Is Nisarga Adhikary and What Did He Achieve?
- Intro: Nisarga Adhikary is a nineteen-year-old cybersecurity researcher, ethical hacker, and software engineer from Siliguri, West Bengal, India.
- He developed an interest through his early fascination with computers, beginning cybersecurity exploration for fun at around age 13.
- He achieved international prominence without a formal college degree by identifying severe security infrastructure flaws.
- He is an expert in full-stack development, Capture The Flag (CTF) challenges, and open-source intelligence.
- His work has involved cybersecurity, OSINT, and threat intelligence.
- Experience: He worked with organisations including the New Delhi Space Society and Wavelength.
- Achievements:
- He developed an early passion for computer science and digital rights. He founded and spearheaded his local Hack Club, contributing broadly to open-source software repositories and engineering projects.
- In September 2024, Nisarga joined the tech firm Skann as a full-time Founding Engineer.
- He transitioned into software engineering roles at Cypherock and Wavelength to build industry experience.
- In February 2026, he examined the Central Board of Secondary Education’s On-Screen Marking (OSM) ecosystem. He responsibly disclosed these to CERT-In.
- By May 2026, he published findings proving an attacker could alter millions of student marks, issues involving authentication, access control and exposure of examination-related information.
- However, CBSE disputed some of the claims, stating that the URL examined was a testing site with sample data.
- Following the CBSE episode, IIT Kanpur’s C3iHub appointed Adhikary as an Open-Source Intelligence (OSINT) and Threat Intelligence Engineer in June 2026.
- C3iHub is associated with cybersecurity and cyber-defence research.
- On 22 September 2026, Adhikary announced that he had been added to the U.S. Department of Justice cybersecurity acknowledgements/Hall of Fame page.
- He audited foreign federal assets. He discovered security vulnerabilities inside the US Department of Defense military infrastructure, triggering a successful validation and remediation process.
What Is the US Department of Justice and “Hall of Fame” Recognition?
- About: The United States Department of Justice (DOJ) is the federal executive department responsible for major aspects of federal law enforcement and legal affairs.
- The Office of the Attorney General was created under the Judiciary Act of 1789, while the Department of Justice itself was established by Congress in June 1870 and formally came into existence on 1 July 1870.
- Administration: The DOJ is headed by the Attorney General of the United States, who is the federal government’s chief law-enforcement officer.
- The Attorney General represents the United States in legal matters, oversees the Department and provides legal advice to the President and executive departments.
- Functions: The Department encompasses numerous important federal law-enforcement components, including the Federal Bureau of Investigation (FBI), Drug Enforcement Administration (DEA), Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF), Bureau of Prisons and U.S. Marshals Service, besides its legal divisions and U.S. Attorneys’ Offices.
- Its operations depend heavily on internet-facing websites, databases, applications and information systems.
- These systems support interactions with the public and law-enforcement community, while the Office of the Chief Information Officer (OCIO) is responsible for information-system security.
- The DOJ operates a formal Vulnerability Disclosure Policy (VDP). It provides guidelines for cybersecurity researchers and members of the public conducting good-faith vulnerability research against publicly accessible DOJ websites and services.
- Its operations depend heavily on internet-facing websites, databases, applications and information systems.
- Recognition: The DoJ Cybersecurity Hall of Fame (or Acknowledgements Page) is an official platform designed to honor ethical white-hat hackers.
- It publicly credits security researchers who bypass vulnerabilities to protect government data rather than exploit it.
- To qualify, independent researchers must identify valid zero-day vulnerabilities or technical loop-holes within the DoJ’s active digital infrastructure. The submission must involve federal web infrastructure or critical law enforcement data networks.
- Researchers must notify DOJ OCIO within 72 hours of discovering a real or potential vulnerability. Testing must be limited to what is necessary to establish that the vulnerability exists.
- Researchers must avoid data exfiltration, privilege escalation, lateral movement, malware, denial-of-service testing, social engineering and disruption of DOJ services.
- A valid report should normally include a description of the vulnerability, potential impact, affected product/version/configuration, reproduction steps, proof-of-concept and suggested mitigation where appropriate.
- Reports can be submitted through the DOJ’s VDP reporting portal or email.
- Upon receiving a report, federal security teams isolate the issue to undergo technical validation.
- Following successful remediation, the Office of the Chief Information Officer indexes the researcher.
- Inductees receive official credit on the government webpage.
India’s Cybersecurity Ecosystem
- Cybersecurity is the practice of protecting systems, networks, programs, devices, and data from digital attacks, theft, or unauthorized access.
- India’s rapidly expanding Digital Public Infrastructure, financial technology, e-governance and online services have increased the importance of cybersecurity.
- Government data recorded 29,44,248 cyber-security incidents in 2025, compared with 20,41,360 in 2024 and 15,92,917 in 2023.
- The Information Technology (IT) Act, 2000 serves as India’s primary legislative backbone for electronic governance and cybersecurity.
- It provides incident-response assistance, coordinates vulnerability handling and supports organisations facing cyber threats.
- Cyber governance must balance two competing requirements: protecting systems from unauthorised exploitation while allowing good-faith security research.
- India’s cybersecurity framework gives special importance to Critical Information Infrastructure (CII).
- The National Critical Information Infrastructure Protection Centre (NCIIPC) is the designated nodal agency for CII protection.
- India’s cybersecurity framework gives special importance to Critical Information Infrastructure (CII).
- Enforced alongside its evolving Digital Personal Data Protection (DPDP) Act & Rules, this legislative framework standardizes how corporate and public entities handle citizen data.
- It mandates strict consent architectures and heavy financial penalties for unnotified data breaches.
- Institutional Mechanisms:
- CERT-In (Computer Emergency Response Team – India): Operating as the national nodal agency for incident response, CERT-In analyzes threat intelligence and issues containment strategies.
- It enforces a strict 6-hour mandatory reporting window for corporate and public cyber incidents. Special divisions like CSIRT-Fin (Financial Sector) and CSIRT-Power act as dedicated arms protecting specialized industries.
- I4C (Indian Cybercrime Coordination Centre): Established under the Ministry of Home Affairs (MHA), the I4C manages nationwide cybercrime reporting and analytics.
- It handles the centralized National Cyber Crime Reporting Portal (cybercrime.gov.in).
- The I4C also hosts the National Cyber Forensic Laboratory to help law enforcement process electronic evidence.
- NCIIPC (National Critical Information Infrastructure Protection Centre): Created under the IT Act’s Section 70A, NCIIPC explicitly shields sectors whose destruction would impact national security or economic health. This includes safeguarding nuclear installations, power grids, defense networks, and banking systems.
- Defense Cyber Agency (DCyA): A tri-service command of the Indian Armed Forces, the DCyA handles military-grade cyber warfare.
- It mitigates state-sponsored threats and develops offensive and defensive digital capabilities across the army, navy, and air force.
- CERT-In (Computer Emergency Response Team – India): Operating as the national nodal agency for incident response, CERT-In analyzes threat intelligence and issues containment strategies.
- Evolving Trends: With UPI processing massive financial volumes, India has faced a surge in automated phishing, fake lookalike banking applications, and Mule Accounts. A prominent challenge includes “Digital Arrest” scams, where criminals impersonate federal officers over video calls to extort money.
- India’s critical physical infrastructure remains vulnerable to highly targeted cyber espionage campaigns. State-aligned actors routinely execute DDoS attacks and deploy ransomware variants (like Akira or WannaCry) to freeze public utilities and banking systems.
- Illicit marketplaces on the Dark Web leverage cryptocurrency channels to anonymize transaction trails, facilitating narcotics smuggling, ransomware-as-a-service (RaaS) leasing, and the illegal trading of leaked citizen datasets.
- India faces a 70% shortage in highly skilled cybersecurity personnel. While academic centers produce engineering graduates, there remains a critical gap in specialized training.
- International Cooperation: In a significant diplomatic move, India officially signed the United Nations Convention Against Cybercrime on the sidelines of the UNGA, establishing mutual legal assistance channels to collect and share electronic evidence across borders.
- India actively coordinates with global partners through dedicated Bilateral Cyber Dialogues with the US, EU, and Japan.
- Under the Quad Cybersecurity Partnership, India coordinates with Australia, Japan, and the US to build resilient software supply chains and combat global ransomware groups.
- Through the Shanghai Cooperation Organisation (SCO) and BRICS Working Groups, India focuses on regional security paradigms. These forums target the prevention of cyber terrorism and establish rules to counter the weaponization of local digital spaces.
- Recommendation: India needs to fully execute its comprehensive National Cyber Security Strategy. This strategy advocates for dedicating a baseline budget (0.25% to 1%) explicitly toward enhancing institutional digital resilience.
- The Ministry of Home Affairs is working to deploy a specialized Cyber Commandos wing across states and Union Territories.
- Recruiting directly from academic centers and the ethical hacking pool will help bridge technical law enforcement gaps.
- Strategic investments in quantum cryptography, secure-by-design software development, and AI-driven automated threat-hunting platforms are critical to safeguarding India’s long-term digital landscape.
- The Ministry of Home Affairs is working to deploy a specialized Cyber Commandos wing across states and Union Territories.
| Cybercrime involves unlawful conduct using computers, networks or digital systems, whereas ethical hacking involves authorised security testing intended to identify and help remediate vulnerabilities. |
Frequently asked questions (FAQs):
1. Who is Nisarga Adhikary?
Nisarga Adhikary is a 19-year-old Indian cybersecurity researcher who identified vulnerabilities in CBSE’s OSM portal and researches government-system security.
2. Why was Nisarga Adhikary named in US DOJ Hall of Fame?
He was recognised after responsibly reporting a critical vulnerability in a major DOJ law-enforcement system, which the DOJ reportedly validated and patched.
3. What flaws did Nisarga Adhikary find in CBSE OSM portal?
He reported exposed answer sheets, hardcoded credentials, weak authentication, client-side OTP verification and access-control vulnerabilities, though CBSE disputed the portal’s production status.
4. How did Nisarga Adhikary enter cybersecurity?
He developed an interest through his early fascination with computers, beginning cybersecurity exploration for fun at around age 13.
5. What is the US Department of Justice Cybersecurity Hall of Fame?
It is a DOJ acknowledgements page recognising researchers who responsibly disclose valid vulnerabilities to the department.
Disclaimer: Information in this article is based on official announcements and public records. Details may evolve over time.